Regulatory Compliance Mapping
When an auditor asks which capabilities satisfy which obligations, the answer usually lives in a spreadsheet that's out of date the moment it's saved. Compliance is a traceability problem, and traceability is what a governed architecture model is built to hold.
How AI-Augmented Architecture handles it
The old way to do compliance in the repository is to record static values on each element: an in-scope flag, a control status, a last-tested date. Someone re-keys them before every audit, and between audits they drift.
The modern way leaves that data in the systems that already hold it. AI connects to your governance, risk and compliance (eGRC) system for obligations, controls and test results, your IT service management (ITSM) system for the systems in scope, your project and portfolio management (PPM) system for remediation projects, and your IT financial management (ITFM) system for what each control costs to run.
The architecture model stitches that data to your capabilities and applications and shows how they relate. Nobody re-types values the eGRC system already holds, so the audit view always shows the current position.
The architect makes the judgment calls about what satisfies an obligation, and AI does the cross-referencing. Questions like "which systems are in scope for this regulation?" start from your application portfolio, with each application tied to the obligations it carries.
Obligations, mapped and traceable
Regulatory obligations are mapped to your capability model as proposed connectors for review.
The architect decides what satisfies each obligation. Automation surfaces candidates and people confirm correctness.
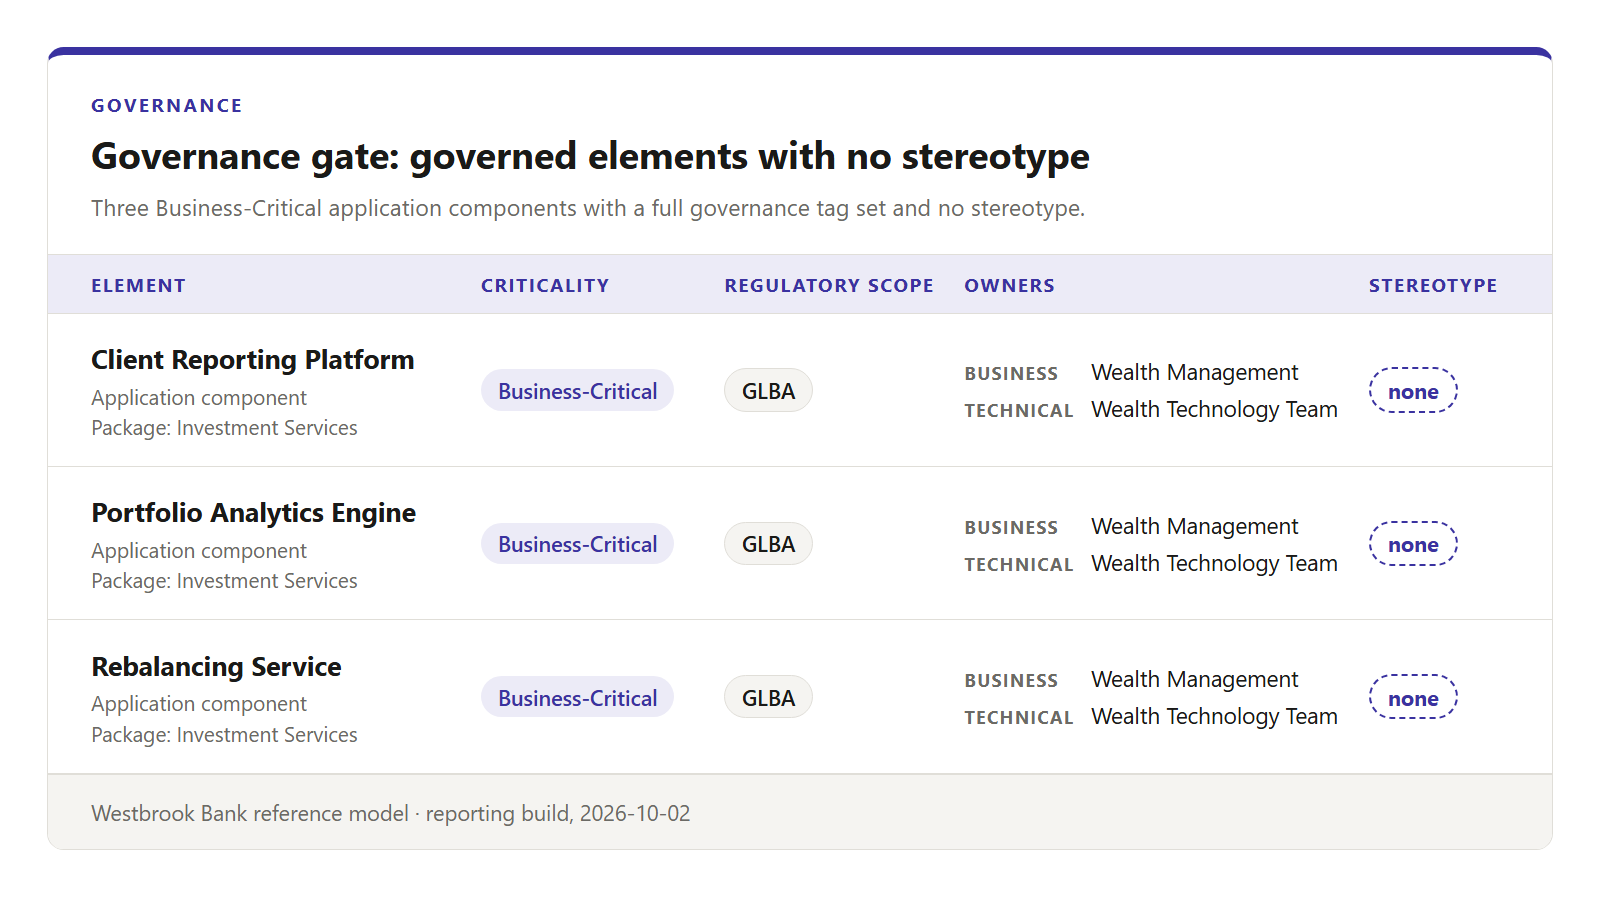
Accepted mappings persist as traceable relationships in the model, and control status comes from the eGRC system, so the audit view stays current.
What a compliance architect can now get done
Compliance mapping is a set of jobs. For each one, the architect states the rules and judges the result.
Mapping obligations to capabilities and applications
Today an architect and a compliance analyst read the regulation, list its requirements in a spreadsheet, and match them to capabilities and systems by hand.
AI-augmented, the architect states the mapping rules, such as what counts as a capability addressing an obligation and what evidence the auditor will expect. AI proposes the connectors between obligations, capabilities and applications, and the architect reviews and accepts them.
The skill is interpreting the obligation, and deciding what counts as satisfying it.
Bringing control status in from the systems that hold it
Today control status and test results are typed into the repository or a spreadsheet in the weeks before each audit.
AI-augmented, the architect names the eGRC system as the source of record for controls and test results, the ITSM system for the systems in scope, and the PPM system for remediation projects. AI connects to them and relates the records to the obligations in the model, and lists anything it could not match.
The skill is knowing which system to believe for which fact, and stating matching rules clearly enough that exceptions are flagged instead of guessed.
Answering the auditor's scoping question
Today "which systems are in scope?" is answered by asking around and assembling a list by hand.
AI-augmented, the architect asks the model which applications support the capabilities tied to the regulation, and reads the answer with the trail of relationships behind it.
The skill is asking a precise question and noticing what the model cannot know, such as a system that was never modeled.
Showing leadership the compliance position
Today the compliance report is rebuilt from the spreadsheet for each committee meeting.
AI-augmented, the architect starts from the decision the committee has to make, such as where to fund remediation first, and describes the view that would inform it. AI builds it on the connected data.
The skill is starting from the decision, and describing the view in terms of that decision.
Which tools help with which job
- Claude + AI Power Tools
Maps obligations to capabilities and applications as proposed connectors, brings control status in from the eGRC system and answers the scoping question on the live repository.
- GitHub Copilot + AI Power Tools
The same mapping and control-status work from VS Code, for architects who already work there.
- Kernaro Assist
Helps map obligations to capabilities from inside Enterprise Architect, as architects model.
- Kernaro AI Hub
Answers the auditor's scoping question from the live model, read-only for the people who ask.
- Prolaborate 6 with AI
Gives the committee a compliance view on the connected data.
- Power BI
The compliance dashboards leadership opens. Kernaro AI Hub is the recommended route for Power BI: it reads the model live through a GraphQL endpoint, with no intermediate database.
- Microsoft 365 Copilot
Lets a committee ask questions of the model in Copilot. It is read-only.
How we help
Train and mentor your architects
Training and mentoring that teach your architects to map obligations into the model this way on your own repository, then stay with them until it sticks.
For ArchitectsBuild the model for you
Consulting services for organizations that are capacity constrained or need results quickly. We build the obligation mappings and the connections to your source systems and hand them over complete and current.
Build the model for youGet your EA data into the tools leaders use
Compliance dashboards for the committee in Power BI or Prolaborate, built on control status that stays in the eGRC system.
Reporting and Power BIDecide where to start, with a plan management will fund
Using the NovoCircle Method, we get leaders and teams to decide where to start, with a plan management will fund and a team ready to deliver it.
Paralysis to a Plan